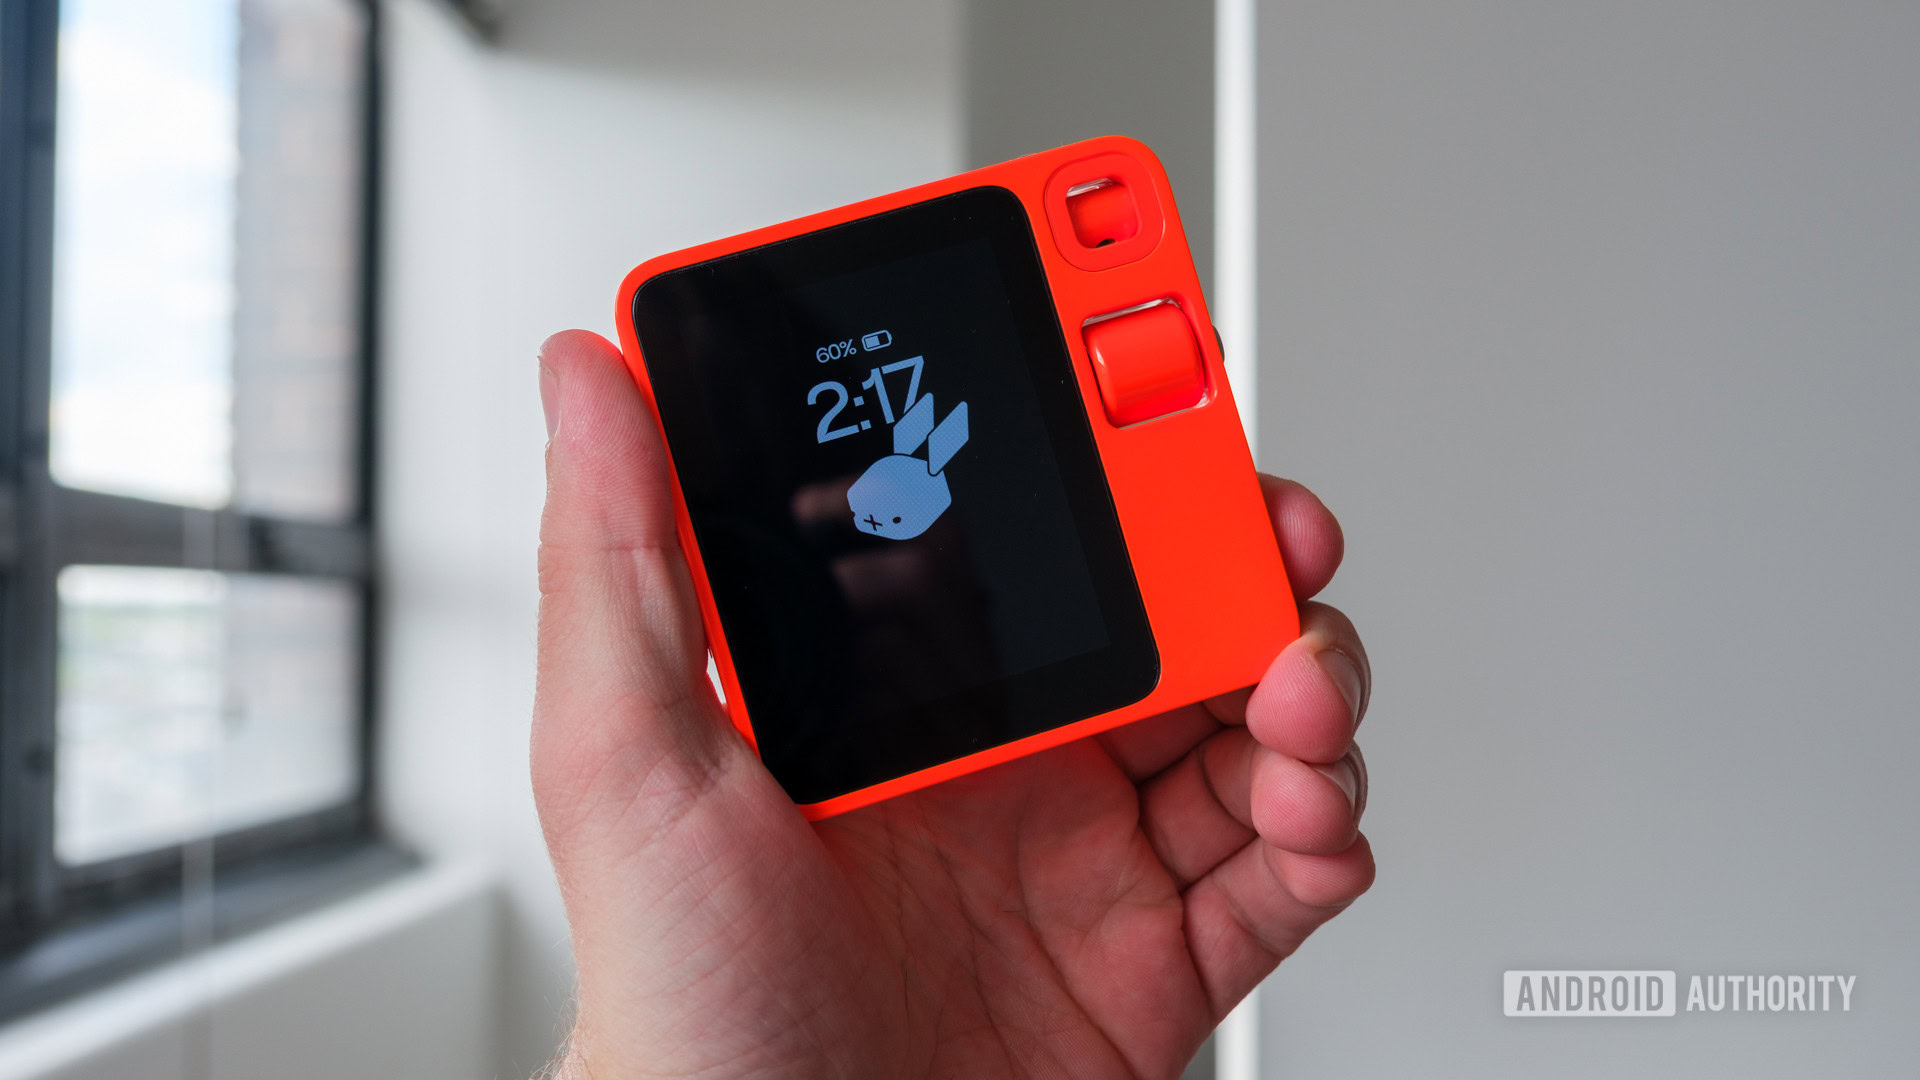
Credit: Ryan Haines / Android Authority
- Researchers have discovered a major vulnerability with the Rabbit codebase.
- This flaw allows malicious actors to read every response any Rabbit R1 gadget has ever issued.
- The team claims Rabbit is aware of the flaw but has chosen to ignore it.
The
Rabbit R1 AI gadget has been underwhelming, overhyped, and unreliable. Unfortunately, it looks like the product has a major vulnerability that Rabbit hasnt fixed yet.
A team of security researchers collectively known as
Rabbitude reported that it gained access to Rabbits codebase on May 16 and discovered several hardcoded API keys. These keys are for two text-to-speech systems (ElevenLabs and Azure), Google Maps, and Yelp.
More...